
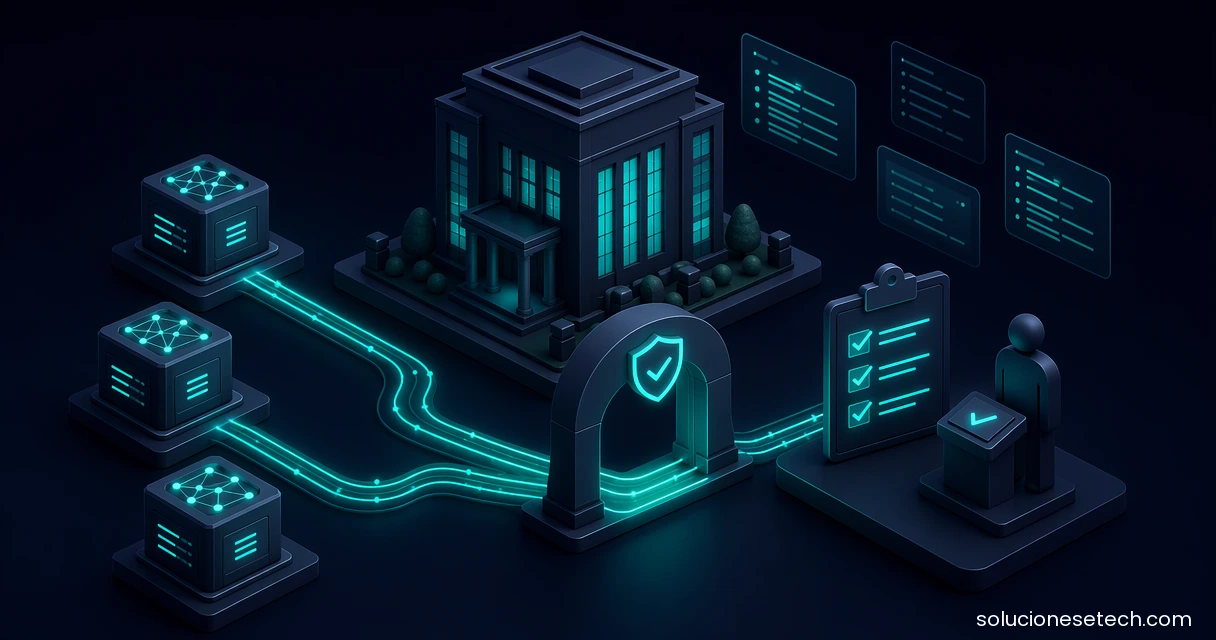
An AI governance framework for regulated companies has to answer four questions from records: which AI tools are in use, which data they reach, who approves what they do, and what evidence remains. Start with an inventory of AI use and one accountable owner per use. In Panama, a September 2026 study of 237 companies found that 39% had no clear owners or processes for AI at all.
Controls, frameworks and metrics are built on top of that inventory, and the policy document comes last. The deadline is set by your next audit: when the question comes, the answer has to come out of a log, and that log only exists if someone designed it in advance.
Why can't AI governance wait any longer?
Adoption is running ahead of control. The study, Elementé's economic activity report as covered by Panamá América (September 10, 2026), also found that 38% manage AI in isolated pockets by department and only 11% have it integrated into operations. These companies already use AI; most of them cannot yet show how they supervise it.
The legal ground is shifting as well. Panama's Law 81 of 2019 requires security measures proportional to risk for personal data, including data that passes through an AI model. For companies with operations or customers in Europe, the EU AI Act, Regulation (EU) 2024/1689, has been in force since August 1, 2024, with obligations phasing in over several years. Even where it does not apply directly, European customers and partners will raise it in due diligence.
What does Panama's AI bill require?
Bill 588 on adaptive AI governance passed its third debate on August 19, 2026. According to the summary published by the firm Pacífica Legal, it calls for meaningful human oversight: a real ability to understand, evaluate, intervene in and reverse AI-assisted decisions, backed by documented processes and verifiable records. As of this article we found no published sanction, so it is not law yet.
It still signals the kind of evidence regulators across Latin America will expect. A signature under an automated decision does not prove oversight; a record of who reviewed it, with what information and what they did, does. Companies that design their controls to leave that record today will not need to rebuild them if the bill is signed.
What should an AI governance framework for regulated companies answer?
A risk committee or an auditor will not ask which model is best. They will ask about control. These are the questions worth being able to answer today, with the evidence that answers each one:
| Auditor question | Evidence that answers it | Red flag |
|---|---|---|
| Which AI tools does the company use? | Inventory of AI use, with owner and date | Tools nobody approved, showing up on a corporate card |
| Which data reaches each model? | Data classification per use case | Customer or personal data pasted into a public chat |
| Who approves what an agent does? | Approval log with name and timestamp | Agents that write, send or publish without human confirmation |
| Who used what, and how much? | Per-call trace, per person and per agent | One API key shared by a whole team |
| What happens if the vendor changes the model? | Controls outside the model, at the access layer | Rules written around one specific brand |
| How is access revoked? | A tested procedure with a measured time | Non-expiring keys sitting in config files |
Any row without evidence is a gap. Most companies find two or three in their first review.
Which reference framework should you use?
There is no need to invent one. The NIST AI Risk Management Framework 1.0, released in January 2023, organizes the work into four functions: govern, map, measure and manage. ISO/IEC 42001:2023 defines a certifiable AI management system that follows the same continual-improvement logic as ISO/IEC 27001.
A company starting out will not adopt either in full in the first month. Use them as a checklist of what an auditor expects and in what order to build it. If you already run an information security management system, build AI governance on its existing risk, change and internal audit processes instead of opening a parallel track.
Which controls work regardless of the model?
Models change versions, prices and terms every few months, and a control tied to one brand has to be rebuilt with each change. The controls that last sit outside the model:
- Identity per person and per agent. Every model call should be attributable to someone. In our implementations we use a model gateway with one key per person and per agent, a budget per key and a trace of every call.
- Sensitive data stays out of the model. Personal or regulated data is resolved server-side after verifying who is asking. The model works with references, not with the data itself.
- Human approval for anything with external effect. Sending, publishing, paying or changing a production system waits for a person, and that approval is logged.
- Provenance for generated content. Code or documents produced by AI carry a mark of what generated them and who reviewed them. Without it, an audit cannot separate human work from automated output.
- Tested revocation. Know how long it takes to cut off a compromised agent. If you have never tested it, the real number is unknown.
We cover the first and third controls in hybrid AI governance: the controls that survive a model swap, and connecting agents without open ports in secure connections for AI agents.
How do you start an AI governance program in 30 days?
A realistic plan for a regulated company that already uses AI, without stopping anyone's work:
- Week 1 — Inventory. List the tools, models and agents in use, including those that never went through IT. Ask each department and check card expenses and browser extensions.
- Week 2 — Classification and owners. For each use, record which data it touches and who is accountable. Flag those that touch personal or customer data.
- Week 3 — The three highest-risk gaps. Pick the three uses with the most exposure and close them: remove data from prompts, split shared keys, require human approval.
- Week 4 — Evidence. Confirm that every control leaves a record you can show. Write the policy last, when it describes what already happens.
A signed policy states intent; a log proves it happened. In an audit, the log carries the weight.
What do companies most often get wrong at the start?
Starting with the document. An acceptable-use policy without an inventory or logs leaves the company where it was, plus one more PDF. The second mistake is governing by tool: approving one brand and assuming that covers everything else. People keep using whatever helps them; governance has to see that use rather than ban it on paper.
The third is keeping AI outside the data governance the company already has. A document classified as confidential should stay confidential when someone pastes it into a chat or an agent reads it. For how Panama's Law 81 maps onto AI environments, see our Law 81 compliance map.
How Soluciones Etech Corp approaches it
From Panama, Soluciones Etech Corp implements AI governance for regulated companies in the financial sector and other industries: which model touches which data, who approves, and what evidence remains. We run it first on our own hybrid AI platform, with frontier models for judgment and local models for volume. See our AI services, or contact us to book the AI governance assessment.